Network security
Firewall policy, network segmentation and traffic analysis, built and broken in an isolated lab rather than read about.
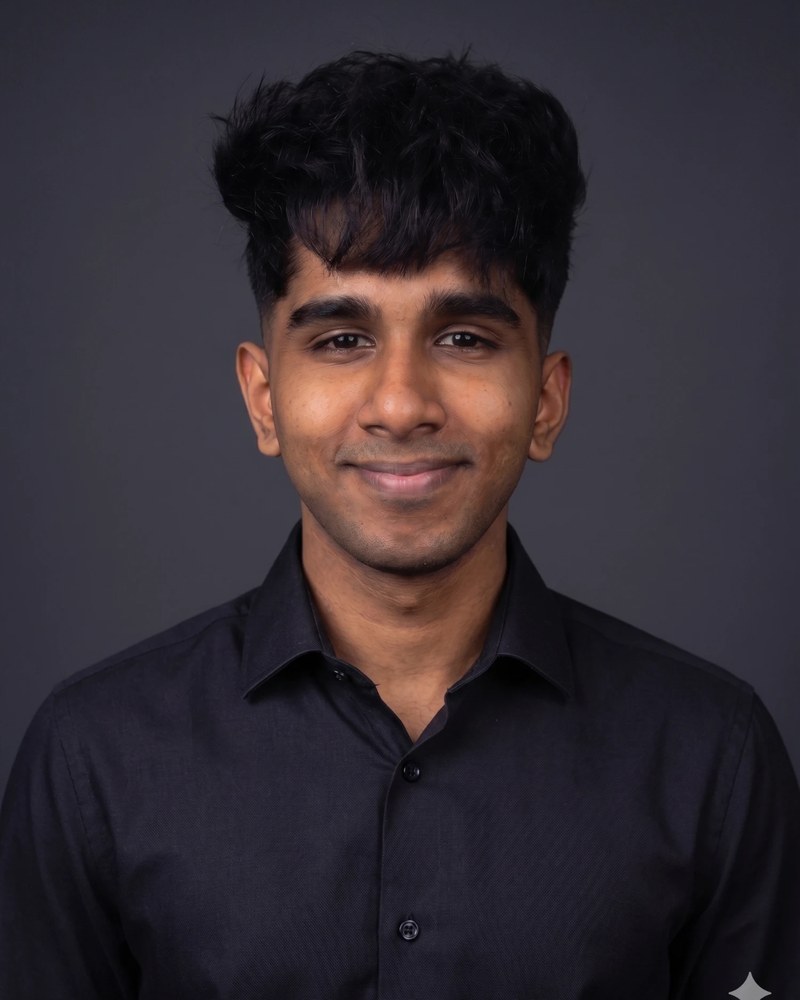
Cyber Security student at CU London and freelance developer, based in Crewkerne and London. I build secure systems and teach people how they get broken.
I am a BSc (Hons) Cyber Security student at CU London, and I work freelance building web applications and testing them. Both halves point the same way: building secure systems, and teaching other people about digital safety.
That second half matters to me. A firewall rule protects one network. Showing a fourteen year old how to recognise a phishing message protects them everywhere, which is why one of my projects is an awareness game built for that age group rather than another scanner.
Right now I am going deeper on pfSense configuration, traffic analysis in Wireshark and Linux administration, alongside algorithm and data structure work in Python.
Education
CU London, Dagenham. January 2025 to present. Elected Course Representative for Cyber Security.
Two disciplines, one toolbox.
Firewall policy, network segmentation and traffic analysis, built and broken in an isolated lab rather than read about.
Cryptosystem implementation and benchmarking, and designing away from security through obscurity.
Front to back, including offline-first apps that keep user data on the device instead of on someone's server.
The environment the rest of the work happens in: Linux administration, scripting, version control and cloud.
Network security, cryptography and web work. Everything here is on GitHub.
An isolated enterprise topology built to enforce strict segmentation. A pfSense boundary firewall routes for an Ubuntu 24.04 workstation that sits on a private internal bus with no direct path to the WAN, so every packet in or out has to pass a stateful policy at the gateway.
A cybersecurity awareness game written for 14 to 16 year olds, teaching them to recognise a phishing attempt from the things that actually give one away. Built as a team project. The hardest part was pitching real attack technique at an audience that has no security vocabulary yet.
A sandboxed cryptosystem implementation for security research and cryptographic benchmarking, written against the principle that real data protection cannot rest on security through obscurity.
A private training log that suggests your next session's exercises and weights from your split and lifting history. No backend and no sign-up: everything stays in localStorage on your own device.
Security decays fast if you only read about it.
Advanced firewall configuration and automated rule management on my own isolated network.
Network traffic analysis. Reading what a capture actually says rather than what you expected it to.
System administration on the workstation and gateway hosts that make up the lab.
Data structures and algorithm work, from graph search to scheduling to thread-safe state.
Segmentation, stateful policy, and the gateway as the enforcement point.
Turning attack technique into something a non-technical audience can act on.
Graph search, scheduling strategies, sorting, and thread-safe shared state.
Running team projects, and representing other students on the course.
Looking for placements and graduate opportunities in security, and open to collaborating on open-source security tools, network monitoring utilities and interactive cybersecurity projects.